Platform
Revocation, CRL and OCSP
Certificate revocation, CRLs, and OCSP.
Revoke a certificate
On Certificates, select a certificate, choose a Revocation reason, and select Revoke. SimpleSCEP immediately republishes the CRL and updates OCSP.
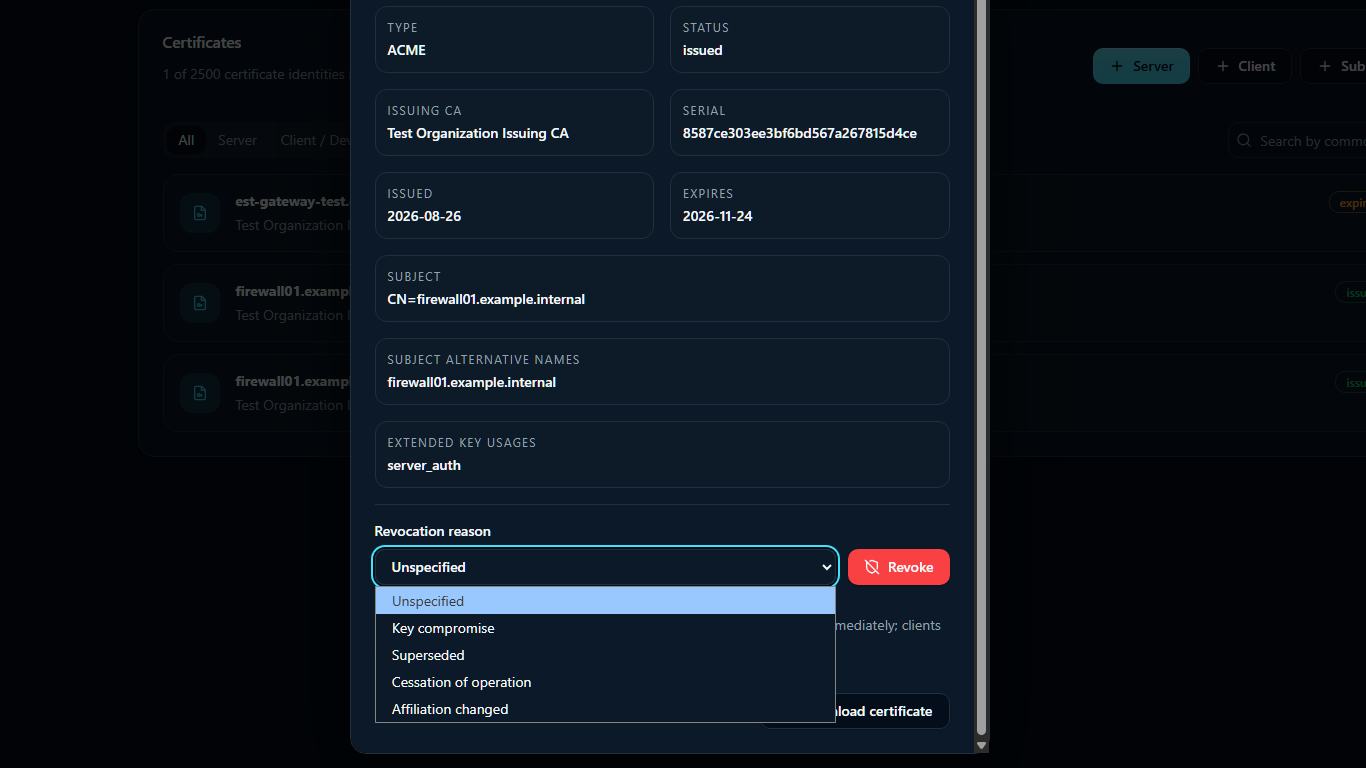
| Reason | Use it when |
|---|---|
| Unspecified | No better answer, or you do not want to disclose one |
| Key compromise | The private key may be in someone else's hands |
| Superseded | Replaced by a new certificate for the same subject |
| Cessation of operation | The subject no longer exists or is decommissioned |
| Affiliation changed | The subject's organizational details are no longer correct |
The reason is included in the CRL. Revocation cannot be undone; reissue the certificate if needed.
Certificates can also be revoked by an ACME client over RFC 8555 §7.6, and through Microsoft Intune. Intune revocations are collected hourly, so they take up to an hour to reach the CRL.
Public endpoints
Each issuing CA publishes at URLs derived from your organization ID and the CA's ID. They require no authentication:
CRL     https://pki.example.com/pki/<organization-id>/<ca-id>/crl
OCSP    https://pki.example.com/pki/<organization-id>/<ca-id>/ocsp
Issuer  https://pki.example.com/pki/<organization-id>/<ca-id>/issuer
Issued certificates include these URLs. Revocation & OCSP shows each CA's URLs, publication times, and revoked serials.
| Endpoint | Details |
|---|---|
| CRL | Served as application/pkix-crl, regenerated when stale, cached until its next update |
| OCSP | Accepts POST with a DER body and GET with a base64-encoded request in the path, as RFC 6960 requires. Responses cached until they expire |
| Issuer | The issuing CA certificate as DER (application/pkix-cert), cached for a day |
Each issuing CA publishes its own CRL.
Freshness
CRLs and OCSP responses are valid for 24 hours and refresh automatically.
Republish CRLs immediately republishes every distribution point. Use it after a bulk change or to test CA signing. Failures appear on the CA row.
Notes
- Only issuing CAs publish CRLs. A root signs nothing but issuing CAs and has no revocation surface of its own.
- Deleting a CA eventually destroys its key, after which its CRL can no longer be republished. Revoke what needs revoking first.
- Deleting an endpoint does not revoke anything it issued — see the deletion sections in SCEP, ACME, and EST.
- Revocations appear in the audit log with the actor, the serial, and the reason.